By ZEISMO ·
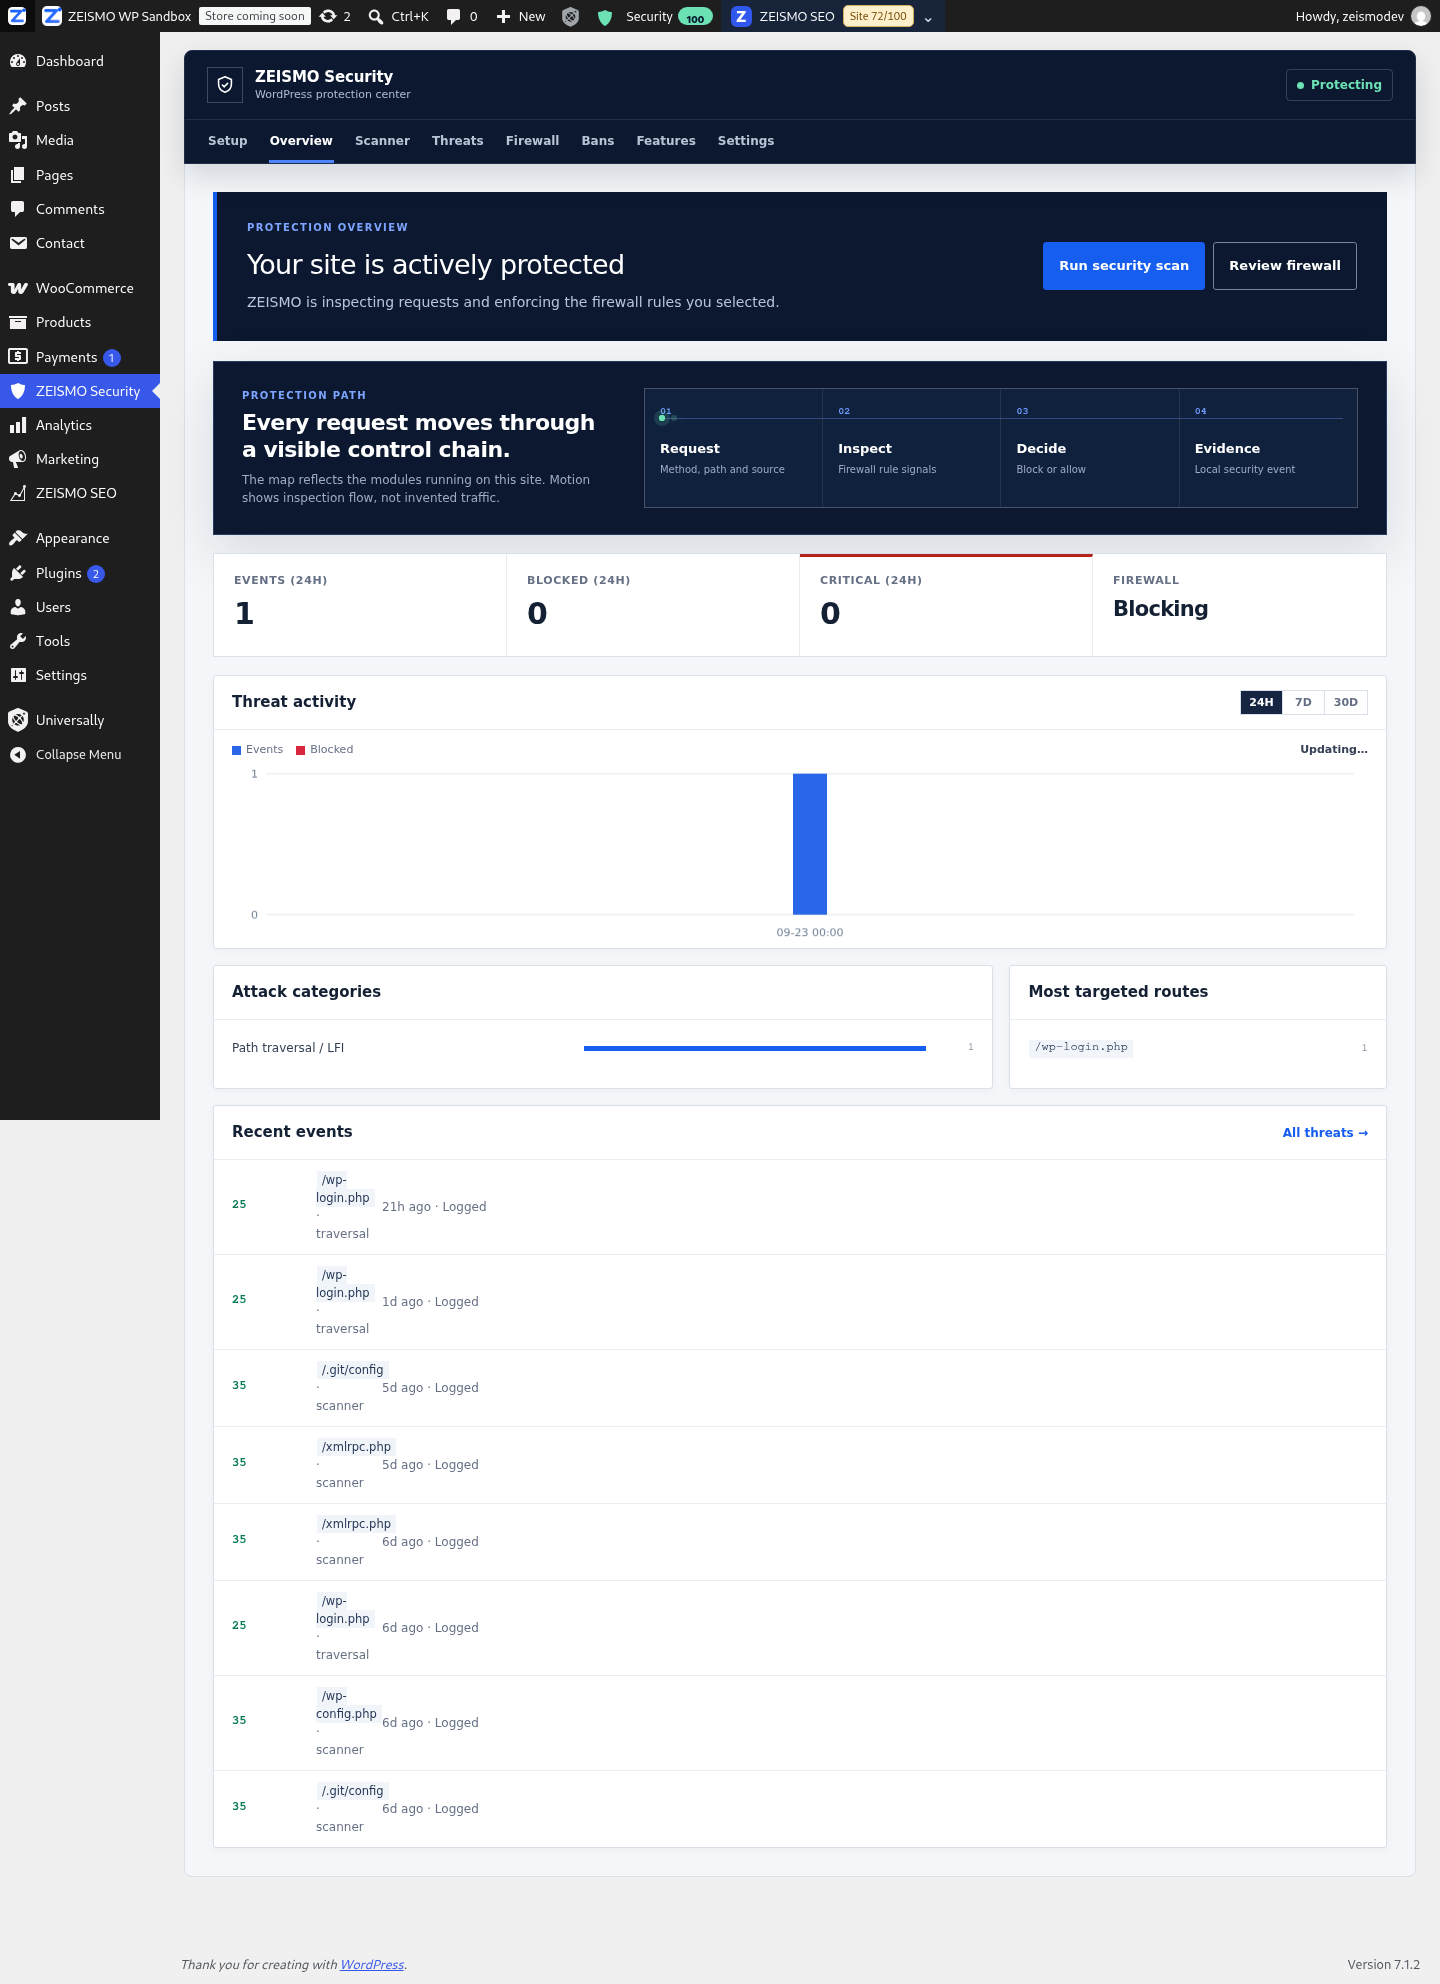
ZEISMO Security 1.0.0 has been submitted to the WordPress.org Plugin Directory under the slug zeismo-security. The automated scan passed. Manual review and approval are still pending.
The submitted edition includes local request monitoring, file integrity and malware pattern checks, login attempt safeguards, IP rules and WordPress hardening. It starts in Monitor mode so administrators can inspect activity before choosing enforcement.
The WordPress.org edition does not require a ZEISMO account or send source files or traffic records to ZEISMO. Scanner findings need review; no security plugin can guarantee that a site will never be compromised.
The marketplace preview includes six authentic screenshots and a complete user guide. Downloads remain closed until WordPress.org approval is verified. This announcement is not an approval or release notice.